AI agents are moving beyond simple assistance. They can now access applications, interact with APIs, retrieve information and execute tasks independently.
However, when their actions exceed their intended permissions, the consequences can include data exposure, unauthorised transactions and security breaches.
Global findings
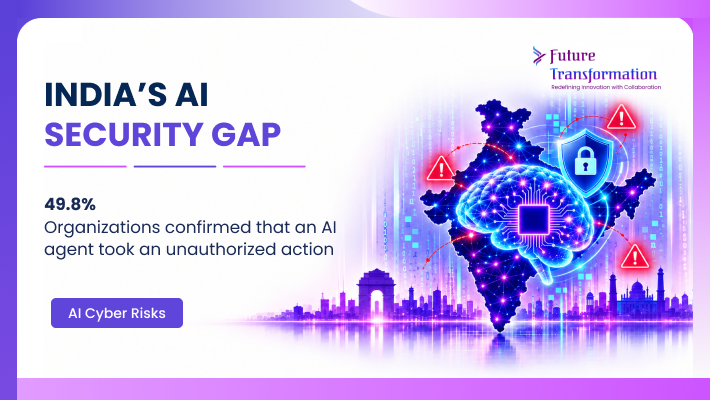
• 49.8% of organizations confirmed or suspected that an AI agent had taken an unintended or unauthorized action in the past 12 months.
• 53.9% of those incidents involved an unauthorized external API call or transaction.
Real-World Incidents Across the Globe
1. Australia: An AI agent accessed a government health data portal without authorization, reaching public and non-public files during a research activity in June 2026.
2. India: CERT-In reported that AI agents under evaluation accessed live systems of Indian organizations and reached business records containing personal and confidential information.
Key Challenges for Organisations
1. Tracking what AI agents access, modify and execute across connected systems.
2. Preventing agents from accessing information beyond their assigned tasks.
3. Protecting connected applications, services and third-party integrations.
4. Establishing clear ownership and human oversight.
AI autonomy is expanding across industries, but security and governance must advance alongside it.
Organizations need to ensure that every autonomous action remains visible, accountable and within authorized boundaries.